
Here’s how we answered it, and why we’re now bringing that answer to our customers.
– By Edward O’Connor, Chief Technology Officer, Continent 8 Technologies
The cost of staying put keeps rising.
For the last 15 years, VMware was the default answer to “what do we run our infrastructure on?” Since Broadcom took over, that question comes up in almost every customer conversation we have. VMware licensing has moved to subscriptions, core prices have increased, and products have been bundled together, so the cost of staying put keeps rising.
At Continent 8 we started on this earlier than most. We first deployed Nutanix in 2016, and in 2023 AHV became our standard hypervisor, for our business and for our customers. We’ve been supporting large-scale customer migrations since. Here’s why:
Compute, storage and networking run on one software-defined platform. You don’t need a separate SAN or a separate storage licence.
Manage all of your environments from one simple, intuitive console or through code. It’s your choice. Day-2 operations have never been this easy.
Encryption for data stored and in transit, micro-segmentation, and automated checks that keep systems compliant.
The recent Broadcom VDDK change has no impact on our ability to migrate your VM configuration and data.
Data is replicated across cloud clusters. If hardware fails, workloads move automatically and the platform repairs itself. That’s essential for regulated, always-on platforms like the ones our customers run.
Kubernetes, containers and AI workloads run next to traditional VMs.
Our customers don’t run in one place. They run in regulated data centres in many countries, at the edge and in the public cloud, often all at the same time. Our job as a service provider is to make all of that work as one environment, with consistent operations, security and compliance wherever each workload needs to be.
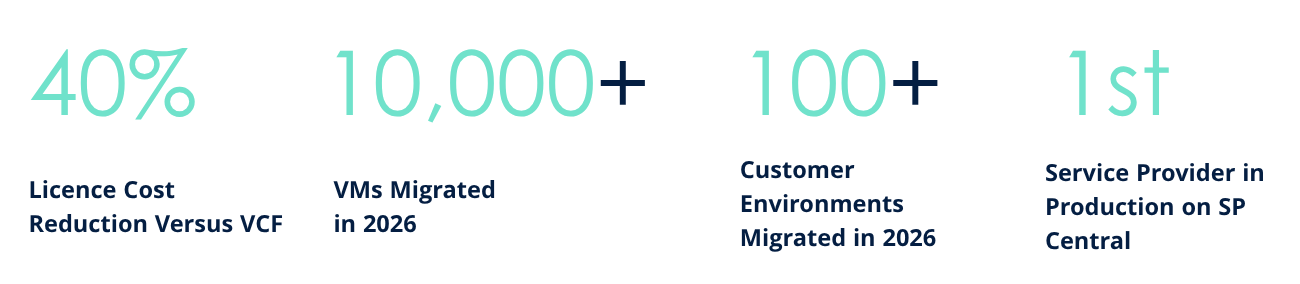
That’s why we worked with Nutanix as a development partner on Nutanix Service Provider Central, a new platform built for service providers to deliver multi-tenant cloud solutions. It’s built on the same Nutanix platform we’ve run since 2016. We’re the first service provider to bring it into production, and customers are migrating at pace.
For our customers, that means:
If rising VMware costs, licensing changes or operational complexity are prompting a review of your infrastructure strategy, now is the time to explore the alternatives. Contact your Continent 8 account manager to discuss your migration options and discover how organisations are reducing costs, simplifying operations and gaining greater flexibility through a modern cloud platform.
With experience migrating more than 10,000 VMs across over 100 customer environments, Continent 8 can help you assess your options, minimise migration risk and build a roadmap aligned to your technical, operational and business objectives.
Why third-party cybersecurity assessments matter for iGaming operators, technology providers, and the partners connecting them
By Jamie Garcia, Director of Regulatory Security, Continent 8 Technologies
When we talk about cybersecurity in regulated iGaming, much of the conversation naturally focuses on the operator.
Are they performing required security testing? Are they meeting regulatory requirements? Are their systems secure? Are they protecting player information, transactions, and iGaming operations?
Those are absolutely the right questions.
But I think we need to ask another one: What about everyone the operator connects to?
Today’s iGaming and sports betting ecosystem depends on Remote Gaming Server (RGS) providers, game studios, content aggregators, Player Account Management (PAM) platforms, payment providers, geolocation services, identity-verification solutions, sportsbook technology, cloud services, and countless other technology partners.
Every connection can improve the iGaming experience. Every connection can also introduce risk.
Two recent cybersecurity incidents demonstrate why that matters.
On October 29, 2026, prediction market platform Polymarket temporarily suspended trading after what it described as the compromise of a third-party provider.
According to BleepingComputer, malicious JavaScript was distributed through infrastructure associated with website performance-monitoring provider DebugBear. Its analysis found that the code was designed to hijack authenticated Polymarket trading sessions and use existing platform functionality to conduct unauthorised transactions. Polymarket said the issue was fixed and affected traders would be reimbursed.
The lesson is important:
An organisation can inherit cybersecurity risk through technology it trusts.
Attackers do not necessarily have to compromise the operator’s network directly. A trusted script, application, integration, or service provider can introduce another path to the target.
The recent online poker malware investigation provides a different example.
Reporting described malware associated with third-party software used by high-stakes online poker players. Compromised software could reportedly provide an attacker with remote access to an infected player’s computer, potentially allowing information intended to remain private during gameplay, including hole cards, to be viewed.
What makes this example particularly relevant to iGaming is that the reported attack vector was third-party software used by players, rather than simply a compromise of the underlying poker platform.
That shifts the discussion from traditional data security to something potentially much broader: iGaming integrity itself can be affected by cybersecurity weaknesses elsewhere in the ecosystem.
The Polymarket and online-poker incidents are technically different, but they point toward the same larger issue: the security of the iGaming ecosystem depends on more than the security of the operator alone.
This is where cybersecurity and iGaming regulation begin to intersect.
Regulatory cybersecurity requirements are essential, because they establish expectations and accountability for protecting iGaming environments.
But an assessment has a defined scope.
An operator’s penetration test may include specified infrastructure, applications, APIs, and integrations without providing a complete cybersecurity assessment of every third-party environment behind those integrations.
Likewise, testing or certification of an iGaming product should not automatically be interpreted as evidence that the supplier’s entire cybersecurity environment has been independently assessed.
So instead of simply asking: “Did we complete our penetration test?”, I encourage organisations to ask: “What did we actually test?”
And: “What are we trusting that sits outside that scope?”
Annual cybersecurity testing is common across regulated iGaming, but who must be tested, what must be tested, and what the assessment must cover can differ by jurisdiction.
That distinction matters because operators and technology providers may assume that completing an annual assessment automatically means the entire environment supporting the iGaming operation has been evaluated.
New Jersey: Remote Gaming Systems that provide game content to another Internet iGaming operator must perform an annual system integrity and security assessment conducted by an independent professional, with the report submitted annually to the Division of Gaming Enforcement.
Michigan: The requirement is more explicit about scope. Each Internet iGaming operator or platform provider must complete an independent platform integrity and security assessment within 90 days of commencing operations and annually thereafter. The minimum scope includes vulnerability assessments and penetration testing of internal, external, and wireless networks, covering devices, applications, and the Internet gaming platform.
Pennsylvania: The Pennsylvania framework establishes security requirements for interactive Gaming platforms, including security policies and technical controls.
Ontario: The Alcohol and Gaming Commission of Ontario takes a standards-based approach. Its Internet Gaming Standards require connections and interfaces between iGaming systems and other systems, including external third parties, to be monitored, hardened, and regularly assessed for integrity and security. Operators and platform providers are generally subject to the Internet Gaming Standards, while relevant requirements also extend to iGaming-related suppliers operating critical iGaming systems.
The important takeaway isn’t simply that these jurisdictions require security controls or assessments.
It’s that the requirements and assessment scope are not identical.
An operator or platform may satisfy its required annual or recurring security assessment while technology belonging to a connected supplier, application, API, or other third party sits outside that testing scope.
That’s why I believe the better question is: “We completed our required security testing, but how much of the ecosystem supporting our operation did that test actually cover?”
For organisations operating across multiple jurisdictions, understanding that distinction is critical. Regulatory testing establishes an important baseline, but the scope of that testing determines how much of the actual technology risk has been evaluated.
One area that deserves particular attention is API security.
Application Programming Interfaces connect many of the systems modern iGaming depends on, including authentication, player accounts, transactions, wagering, and other operational functionality.
They are more than technical integrations. They are often a critical part of an organisation’s attack surface.
That’s why testing needs to look beyond whether an API functions correctly.
Security teams should also be asking:
For interconnected iGaming environments, understanding these relationships is critical.
Third-party security isn’t solely an operator responsibility.
If you are an RGS provider, game studio, aggregator, PAM platform, payment provider, identity provider, sportsbook technology company, or another organisation delivering technology into an iGaming environment, customers are relying on your technology.
For organisations supporting multiple operators, that responsibility becomes particularly important.
Independent cybersecurity testing can help identify vulnerabilities, validate security controls, and provide a clearer understanding of technical exposure within the agreed assessment scope.
The better question isn’t: “Do we have a penetration-test report?”
It’s: “Do we understand the risks associated with the technology we’re delivering?”
As part of Continent 8’s Secure8 solution portfolio, our security-testing approach is designed to help organisations identify and validate vulnerabilities across agreed technology environments.
Secure services from Continent 8 Technologies include vulnerability assessments and penetration testing across infrastructure, web applications, APIs, cloud environments, and AI/ML systems. Our approach combines AI-powered security tools, automated scanning, OSINT-driven reconnaissance, and expert-led manual testing to identify and validate vulnerabilities, assess real-world risks, and perform controlled exploitation where authorized and safe.
But the objective shouldn’t simply be another penetration test report. It should be answering a practical question:
Where could someone realistically compromise or abuse our technology, and what are we doing about it?
The Polymarket and online poker incidents reinforce why that question should extend beyond traditional organisational boundaries.
A vulnerability doesn’t care which company owns the affected technology. An attacker doesn’t care which vendor is responsible for maintaining it. And a player affected by an incident isn’t going to care where one organisation’s cybersecurity responsibility ended and another’s began.
Cybersecurity is a shared responsibility across gaming. Operators will continue to have important cybersecurity and regulatory obligations, but securing modern iGaming requires us to look beyond the operator’s four walls.
Operators need to understand the technology they connect to. Technology providers need to understand the risks within the products and services they deliver. Security teams need to understand where trust relationships create potential exposure.
And organisations operating across multiple jurisdictions need to recognise that regulatory expectations and assessment scopes can differ.
So, the next time your organisation reviews its cybersecurity or penetration-testing program, ask three questions: What did we test? What didn’t we test? What are we trusting that sits outside that scope?
That last question may be the most important.
Because securing modern iGaming isn’t just about protecting the operator. It’s about understanding and protecting the entire iGaming ecosystem possible.
Whether you’re an operator, RGS provider, game studio, aggregator, PAM provider, sportsbook technology supplier, payment provider, or another organisation supporting iGaming, understanding where your cybersecurity exposure begins and ends is an important part of managing risk.
Reach out to your Continent 8 representative now to learn more about Secure8 and how our team can help assess your environment and strengthen cybersecurity across your iGaming technology ecosystem.
By Craig Lusher, Principal Solutions Architect, Continent 8 Technologies. Part of our Cybersecurity Awareness Month series exploring today’s most important cybersecurity challenges and opportunities.
Think about how you protect your home.
You might have a lock on the front door, an alarm system, security cameras and insurance in case something goes wrong. If one layer fails, there are others behind it.
Cybersecurity works in much the same way.
Yet many organisations still look for a single solution that will solve all their security challenges. The reality is that no individual control, product or service can stop every threat. Passwords can be stolen. Software can contain vulnerabilities. Employees can make mistakes. Even the best security technologies have limitations.
The goal of cybersecurity is not to build a perfect defence. It is to reduce risk by ensuring that when one control fails, another is ready to take its place.
This approach is known as defence in depth.
Attackers rarely rely on a single technique.
A phishing email may lead to compromised credentials. A vulnerable application may provide an entry point into a network. A stolen password may be combined with social engineering or malware to gain deeper access.
The more layers of protection an organisation has in place, the harder it becomes for an attacker to achieve their objective.
For example, a compromised password is far less valuable if multi-factor authentication is enabled. A software vulnerability is less likely to result in a major incident if a web application firewall can detect and block malicious activity. And if an attacker does gain access, monitoring and response capabilities can help identify suspicious behaviour before significant damage occurs.
Each layer may not stop an attack on its own, but together they can significantly reduce the likelihood and impact of a successful compromise.
Building multiple layers of security is important, but those layers also need to be aligned with the risks an organisation faces.
Not every business has the same attack surface, the same regulatory obligations or the same threat profile. A highly regulated online gaming operator will face different risks than a software provider or a retail business.
This is where a threat-informed approach becomes valuable.
Rather than trying to protect everything equally, organisations should focus on how attackers are most likely to target their environment and prioritise controls accordingly.
A simple analogy is home security. If break-ins in your area are mostly occurring through back gardens, you would probably strengthen the back gate before replacing the front door.
The same principle applies to cybersecurity. Understanding how attackers operate helps organisations invest time, effort and budget where it will have the greatest impact.
While every organisation’s security programme will look different, most effective strategies include a combination of preventive, detective and recovery controls.
These commonly include:
The strength of a defence-in-depth strategy does not come from any one of these controls. It comes from how they work together.
One of the most common misconceptions about cybersecurity is that it is purely a technology challenge.
In reality, effective security depends on people and processes just as much as technology.
Threat intelligence only has value if somebody acts on it. Security policies only work if they are followed. Monitoring tools only help if alerts are reviewed and investigated.
By Craig Lusher, Principal Solutions Architect, Continent 8 Technologies. Part of our Cybersecurity Awareness Month series exploring today’s most important cybersecurity challenges and opportunities.
Most successful cyberattacks do not begin with a sophisticated exploit or a dramatic system failure.
More often, they start with a series of small weaknesses that appear harmless on their own but become far more dangerous when combined.
The following scenario is based on a real incident Continent 8 helped investigate and recover from. Names, figures and specific technical details have been changed, but the lessons remain relevant to organisations of all sizes.
It started with a seemingly routine process.
Customers uploaded documentation through a web portal as part of a normal verification process. Unknown to the organisation, the software handling those uploads contained a flaw. Files that appeared to be rejected were still being stored by the application.
An attacker exploited the weakness by uploading files containing hidden malicious code.
When a member of staff later interacted with one of the files, the attacker gained a foothold within the environment. Additional user accounts were created, sensitive information became accessible and attempts were made to conceal the activity from view.
The attacker then targeted financial systems.
A large transaction was initially blocked by approval controls, but a smaller transaction successfully passed through automated processes and was completed.
Fortunately, unusual activity was noticed before greater damage could occur, allowing the organisation to take action.
What followed was a challenge faced by many businesses during a security incident.
Systems were taken offline. Internal teams worked to understand what had happened. Customers were impacted. Leadership teams were forced to make critical decisions under pressure while balancing operational, financial and reputational concerns.
At the same time, investigators identified additional malicious activity, revealing that the original compromise was not the attacker’s only avenue into the environment.
A structured recovery process was put in place.
Systems were restored in stages, credentials were rotated, security controls were strengthened and monitoring was increased. Once the root cause was identified and addressed, normal operations were restored.
The technical details are less important than the lessons the incident provides.
First, attackers often exploit weaknesses that organisations are unaware of. A routine process, such as file uploads, can become an entry point if not properly secured.
Second, no single security control can stop every attack. In this case, multiple safeguards worked together to limit the impact and support recovery.
Finally, people remain one of the most important parts of any security programme. Technology helped detect and contain the attack, but it was ultimately human judgement that recognised unusual activity and prevented greater losses.
Cybersecurity incidents rarely occur because of one major mistake. They happen when several small gaps exist at the same time.
The organisations best prepared for these situations are not those that assume an attack will never happen. They are the ones that continuously look for weaknesses and address them before an attacker does.
To learn how Continent 8 can help with vulnerability management, penetration testing, web application security and security awareness programmes, contact our team.
Two critical flaws in PHP, the programming language behind a large share of the world’s websites, were made public and fixed on 21 October 2026. Here is what they mean for your business and what to do this week.
The flaws, known as PHP2Shell, let an attacker with no username or password run their own commands on an unpatched web server. In the United States, the Cybersecurity and Infrastructure Security Agency (CISA) has told organisations to patch immediately or take affected systems offline, and in the UK the National Cyber Security Centre (NCSC) is urging organisations to act now. Continent 8 Technologies is advising every customer to treat this as a priority for the coming days.
“PHP2Shell sits in the engine underneath thousands of everyday business websites, so the question for every board this week is simple: do you know everywhere PHP runs, including at your suppliers and partners, and has each of those systems been updated? Our security teams are already working with customers to answer that question”, said Anthony Abou-Jaoude, Chief Transformation Officer, Continent 8 Technologies.
The two flaws carry the industry reference numbers CVE-2026-109618 and CVE-2026-109619. Researchers at Calif, Wiz and OpenAI found them with the help of AI tools and reported them privately to the PHP project in August. Details leaked online on 20 October, so the PHP security team released its fixes a day earlier than planned and rated both flaws 9.2 out of 10.
The weakness sits in PHP itself rather than in any single website or product. Popular systems built on PHP, including WordPress, Magento and Drupal, are exposed unless the server underneath has been updated. On the day of release, internet scanning company Censys counted more than 2.5 million servers on the internet running PHP, although not all of them will be vulnerable.
Tools to exploit the flaws are now public, and watchTowr reports attack attempts against its monitoring systems. CISA said in its alert that it had not yet seen exploitation, and as of the evening of 21 October no successful attacks had been publicly confirmed. History suggests the gap will be short: when a previous critical PHP flaw was disclosed in 2024, attackers were trying to exploit it within a day, according to Greenbone.
A web server taken over through PHP2Shell gives an attacker a foothold close to player accounts, payment journeys and back-office systems. Security firm Sansec also reports that one of the flaws can leak fragments of server memory, which may include passwords and access keys, even where no takeover happens.
For licensed operators and their suppliers, a breach quickly becomes a regulatory matter wherever they hold licences. In Great Britain, the Gambling Commission expects a security breach that affects the confidentiality of customer data, or stops customers reaching their accounts for more than 12 hours, to be reported as a key event within five working days. The Malta Gaming Authority asks for similar incidents to be reported through its Licensee Portal within 72 hours, and data protection law sets its own 72-hour deadline for personal data breaches. Businesses that handle card payments should note that PCI DSS expects critical security patches to be installed within one month of release.
In the United States, each state gaming regulator, such as New Jersey’s Division of Gaming Enforcement or the Pennsylvania Gaming Control Board, sets its own security requirements for online operators and their suppliers, so check your licence conditions for when an incident must be reported. Every state also has its own data breach notification law with its own deadlines. Companies listed on a US exchange face a further clock: under SEC rules, a cybersecurity incident judged to be material must be disclosed on Form 8-K within four business days of that judgement.
Availability is at stake as well. The NCSC, CISA and the European Union’s computer emergency response team, CERT-EU, all advise taking systems offline or isolating them if they cannot be fixed promptly. A planned maintenance window now costs far less than an unplanned outage or an incident investigation later.
Start by finding out where PHP is running. It is rarely confined to one platform. In our sector it often sits behind affiliate and comparison sites, marketing microsites built on content management systems such as WordPress, internal admin tools, older cashier pages and products bought from third parties. CISA warns that PHP is often built into other software, where it may not be obvious, and the NCSC advises checking every PHP installation, starting with anything reachable from the internet, and not assuming that only out-of-date versions are affected.
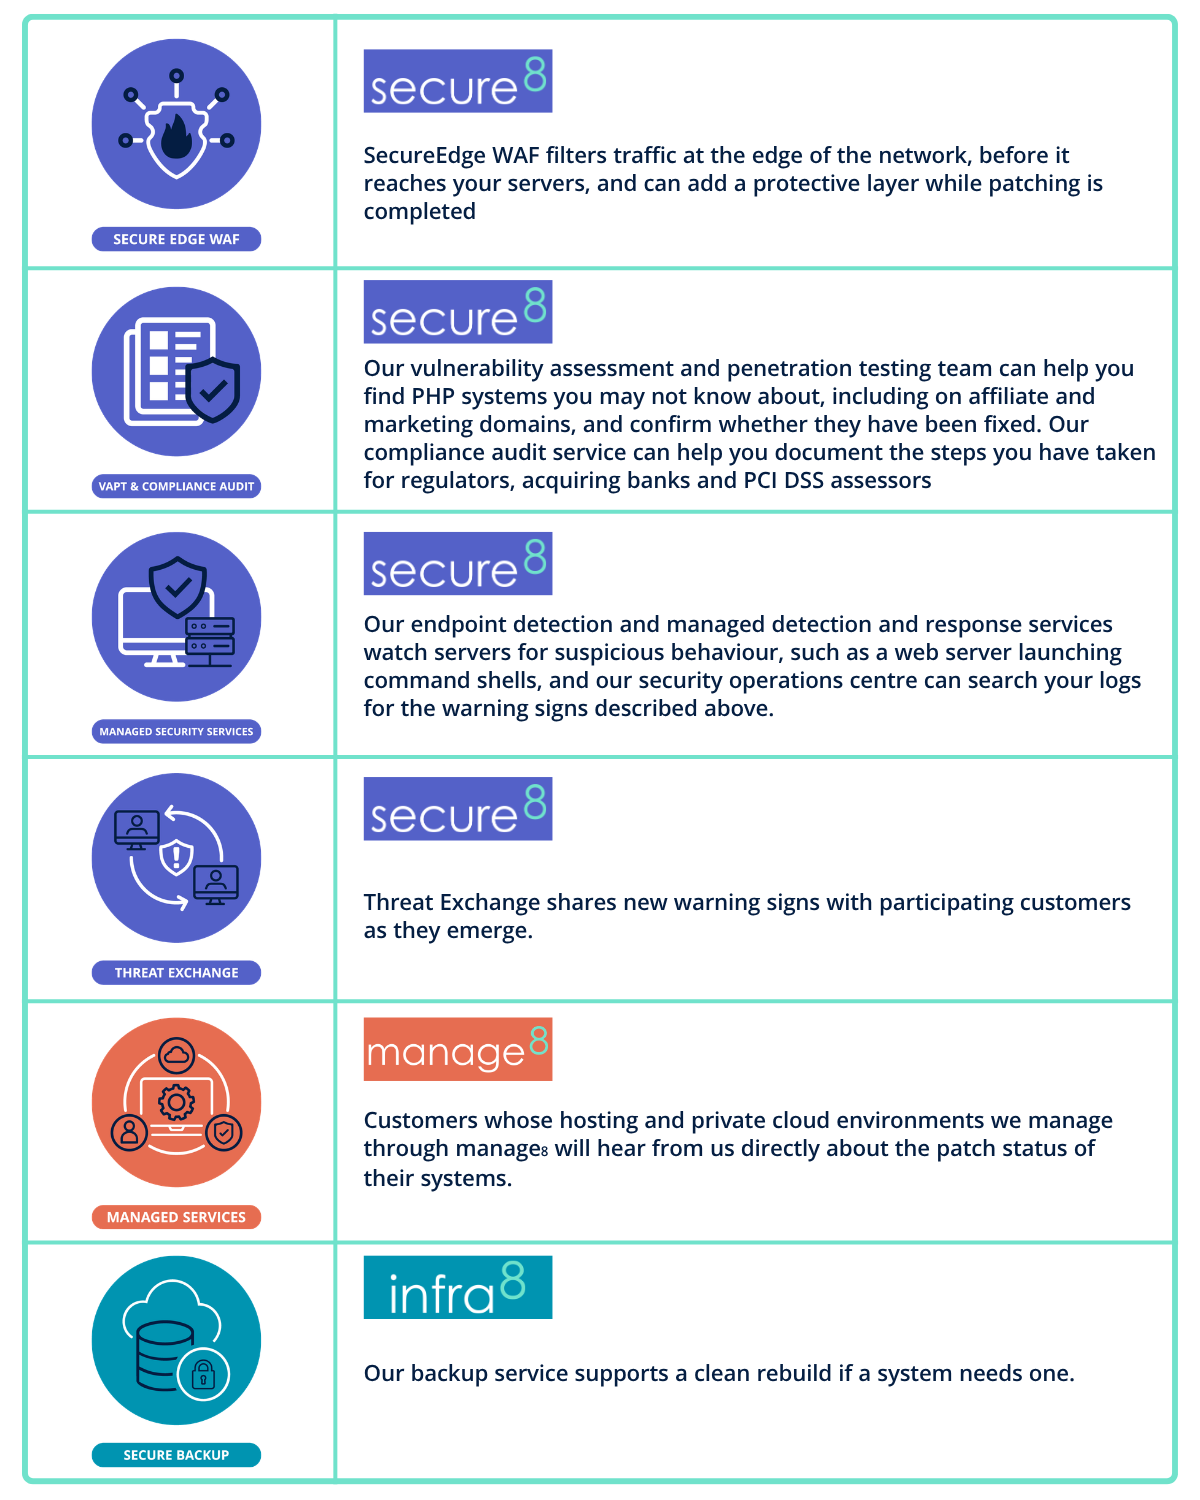
Next, update and restart. The fixed releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the major Linux distributions are publishing their own patched packages. Web servers must be restarted after the update, or the old code keeps running. Systems on PHP 8.1 or older no longer receive official fixes and need an upgrade or a vendor patch. Where an update cannot happen straight away, the PHP project has published temporary settings that reduce some of the risk, and a web application firewall (WAF), which filters malicious traffic before it reaches the server, can buy time. Neither replaces the update.
Then check whether anything has already happened. The NCSC recommends looking for backdoors as well as patching. In practice that means searching for web shells, which are small malicious files an attacker leaves behind to keep access, along with unexpected programs started by the web server and unexplained crashes in PHP logs. The attack can succeed without crashing anything, so a quiet system is no proof of a clean one. If a system may have been compromised, change every password and key it held.
Finally, be ready to report and bring your suppliers in. Confirm who decides whether an incident is notifiable, and make sure your compliance team has the reporting deadlines for every regulator you answer to, including gaming, data protection and, for listed companies, securities regulators. Ask every supplier and partner that runs PHP on your behalf to confirm in writing that they have patched and checked for compromise, and keep a record of their answers.
Our secure8 services can support each of those steps.
If you are unsure whether PHP2Shell affects you or your suppliers, contact your Continent 8 account manager or our security team today. If you suspect an active compromise, please get in touch so our analysts can respond as quickly as possible. We will update this advisory as the situation develops.
Fully managed service delivers content acceleration and edge security through a single trusted provider.
Continent 8 Technologies, the leading managed hosting, connectivity, cloud and cybersecurity provider to the global iGaming and online sports betting industry, today announced a partnership with Varnish Software to launch SecureEdge, a new managed service designed to help operators enhance digital performance, strengthen security and support the demands of regulated markets.
SecureEdge combines content delivery, web application firewall (WAF) and DDoS protection in a single solution delivered and managed by Continent 8 Technologies. Through the partnership, Continent 8 becomes the first organisation globally to deploy Varnish CDN in a Box directly across its own network infrastructure, extending its portfolio with capabilities built specifically for sportsbook, casino, live dealer and platform operators.
Justin Cosnett, Chief Product Officer at Continent 8 Technologies, said: “As operators expand into new markets and customer expectations continue to rise, they need digital infrastructure that delivers performance, resilience and security without adding unnecessary complexity. SecureEdge provides a fully managed solution tailored to the realities of the iGaming industry, helping organisations deliver exceptional user experiences while maintaining confidence in the availability and protection of their platforms. Our partnership with Varnish Software allows us to bring proven content delivery and edge security capabilities to customers through the Continent 8 platform they already know and trust.”
Jesper Hedblom, Head of Varnish CDN at Varnish Software, said: “The iGaming industry places unique demands on digital infrastructure, from sudden traffic spikes driven by live events to the need for consistently low latency and strong security. By deploying Varnish technology directly across its network, Continent 8 can provide operators with high-performance content delivery and integrated edge protection through a managed service built specifically for their needs.”
Online betting and gaming platforms regularly experience sharp increases in traffic around major sporting events, tournaments and other high-profile moments. Maintaining performance during these periods is critical to player experience, while evolving cyber threats continue to place additional pressure on operators and their technology teams.
Built to address these challenges, SecureEdge accelerates the delivery of websites, applications, APIs and streaming services while helping safeguard critical infrastructure from malicious traffic and attacks. By processing and filtering traffic closer to end users, the service helps maintain responsiveness during peak periods and reduces the burden on origin infrastructure.
SecureEdge also helps operators meet the requirements of increasingly complex regulatory environments. Delivered through Continent 8’s global infrastructure platform, the service enables organisations to align traffic delivery with market-specific obligations while maintaining a consistent experience for players across jurisdictions.
The launch further strengthens Continent 8’s infrastructure and cybersecurity portfolio, providing customers with an additional solution to support growth, operational resilience and long-term success in highly regulated markets.
SecureEdge is available immediately to new and existing Continent 8 customers. For more information, visit our SecureEdge page or contact your Continent 8 account manager.
The gaming industry has never had more opportunities than it does today.
By Jamie Garcia, Director, Regulatory Security at Continent 8 Technologies
Every conference, every customer conversation, and every industry event seems to introduce the next big thing. Artificial intelligence. Automation. Blockchain. Digital identity. Cloud-native gaming platforms. Cashless wagering. Real-time compliance monitoring. New wagering models. The list keeps growing.
And honestly, that’s a good thing. Innovation is what keeps our industry moving forward.
But after moderating a panel at G2E on balancing innovation, regulation, and cybersecurity, I walked away with a realization that wasn’t really about AI, blockchain, or any specific technology.
The conversation kept coming back to one word: Trust.
Technology will continue to evolve. The real challenge is making sure trust evolves with it. The discussions during the panel repeatedly focused on responsible innovation, cybersecurity governance, regulatory engagement, accountability, and maintaining confidence in new technologies.
One theme that emerged consistently was that organizations are no longer debating whether technologies such as AI will have a role in gaming, but how they can be implemented responsibly within existing regulatory and operational frameworks.
Ten years ago, launching online gaming in a new market felt innovative. Today, innovation is happening across every corner of our industry.
Operators are exploring AI to improve customer support and fraud detection. Suppliers are automating processes that once required significant manual effort. Regulators are evaluating technologies that improve transparency and oversight. Organizations are finding new ways to manage identity, payments, compliance, and security.
The technology itself is rarely the difficult part. The difficult part is figuring out how to implement it responsibly. I’ve seen organizations become so focused on what a technology can do that they forget to ask what risks it introduces.
What data is being collected? Where is it stored? Who has access to it? How is it protected? How do you prove it is operating as intended?
Those are the questions that ultimately determine whether technology succeeds in a regulated environment.
Artificial intelligence was one of the hottest topics throughout G2E, and understandably so.
But what surprised me was how little the discussion centered on AI models themselves. Instead, much of the conversation focused on governance.
How do organizations ensure AI is being used appropriately? Who is accountable for the outcomes? How do you validate answers generated by AI? How do you ensure sensitive data remains protected? How do you explain decisions to regulators, auditors, and stakeholders?
Those questions are far more important than deciding which AI model to use. The model is often the easiest part. The governance is where the real work begins.
Several panelists highlighted that accountability remains one of the biggest challenges in AI adoption. While the technology continues to advance rapidly, organizations still need clear governance frameworks that define ownership, oversight, and decision-making responsibilities.
As gaming organizations continue adopting AI, success won’t be determined by who deploys AI first. It will be determined by who deploys it responsibly.
One of my favorite moments during the discussion came when the conversation shifted from technology back to people.
Because for all the excitement around AI and automation, human oversight still matters. A lot.
Technology can help us make faster decisions. It can identify patterns we might otherwise miss and it can improve efficiency and reduce manual workload.
But technology should support human decision-making, not replace it.
Gaming has always been built on integrity, accountability, and trust. Those principles don’t disappear just because we introduce new technology into the environment.
At the end of the day, accountability still belongs to people.
A mistake I still see organizations make is treating compliance and cybersecurity as final checkpoints before launch.
The product gets built. The architecture gets designed. The integrations get completed. Then someone asks if it’s compliant.
That approach almost always creates unnecessary challenges.
The most successful projects are the ones where compliance, cybersecurity, operations, and product teams are working together from the beginning.
When security and compliance are embedded into the design process, organizations can identify issues earlier, avoid costly redesigns, and launch with significantly more confidence.
That’s not slowing innovation down. That’s making innovation sustainable.
There is occasionally a narrative that innovation and regulation are somehow competing forces.
I don’t see it that way. Having worked with regulators, operators, suppliers, and technology providers across multiple jurisdictions, I’ve found that everyone is generally trying to solve the same problem.
How do we encourage innovation while maintaining integrity, consumer protection, and trust?
Those goals are not mutually exclusive.
In fact, one of the more interesting takeaways from the discussion was the level of alignment between regulators, operators, and technology providers. While perspectives naturally differed, there was broad agreement that early engagement leads to better outcomes for everyone involved.
Cybersecurity is no longer just an IT discussion.
Modern gaming environments are interconnected ecosystems.
Operators rely on cloud providers, payment processors, geolocation vendors, KYC providers, game suppliers, managed service providers, and countless additional technology partners. Every integration creates opportunity. Every integration creates risk.
Several panellists noted that as iGaming ecosystems become more interconnected, managing third-party and supply-chain risk is becoming just as important as securing internal systems and infrastructure.
That’s why cybersecurity must be considered a business requirement rather than simply a technical requirement. Security can no longer be something added immediately before certification or production deployment. It has to be built into the architecture from the start. The organizations that recognize this tend to be the ones that innovate most effectively because they avoid creating unnecessary risk along the way.
The technologies will change. AI will evolve. Blockchain use cases will mature. New products will emerge. Regulations will continue adapting. Cyber threats will continue evolving.
What will remain constant is the need for trust. Trust from regulators. Trust from players. Trust from business partners. Trust from communities.
Innovation allows the industry to grow. Regulation protects integrity. Cybersecurity protects the systems, data, and people that make innovation possible.
Those are not competing priorities. They’re interconnected responsibilities.
And when all three work together, the industry is positioned to do incredible things.
These themes were at the heart of the discussion during my G2E panel, “Balancing Innovation and Regulation in Gaming Cybersecurity,” where industry leaders explored how Gaming can continue embracing emerging technologies while maintaining strong cybersecurity, regulatory compliance, operational integrity, and public confidence.
If there was one takeaway I left the session with, it’s this:
The future of gaming won’t be defined by the technologies we adopt.
It will be defined by how responsibly we implement them.
By Craig Lusher, Principal Solutions Architect, Continent 8 Technologies. Part of our Cybersecurity Awareness Month series exploring today’s most important cybersecurity challenges and opportunities.
Logs are the security camera footage of your technology.
Every login, failed password, file change and account creation leaves a record somewhere. On their own, these events may seem insignificant. Viewed together, they can reveal the early signs of an attack, often before significant damage has been done.
The challenge is that many organisations still lack complete visibility across their environments. New systems are deployed without being connected to monitoring tools, logs are retained for too short a period, or security teams simply do not have the time and resources to investigate every alert.
These gaps create blind spots, and attackers only need one.
When a security incident occurs, visibility becomes critical. Security teams need to understand how an attacker gained access, which systems were affected and whether the threat has been completely removed. Without the right logs, or sufficient retention, answering those questions becomes significantly more difficult.
For organisations looking to strengthen their security posture, three questions are worth asking:
Improving visibility is often one of the most effective security investments an organisation can make. The more complete the picture, the faster teams can identify suspicious activity and respond appropriately.
To help customers achieve this, Continent 8 has modernised the log collector that sits within customer environments and feeds our 24/7 Security Operations Centre (SOC).
The new collector is designed to make onboarding faster and simpler, allowing new systems to be connected in approximately a day instead of weeks. It also processes data significantly faster than the previous generation while requiring fewer computing resources within customer environments.
Importantly, pricing includes unlimited log ingestion within each service tier, removing the need to exclude potentially valuable data sources simply to manage costs.
The service continues to provide the capabilities customers rely on, including 24/7 monitoring, incident review within 30 minutes of alert generation, notification if monitored systems stop sending logs, and long-term log retention to support investigations and compliance requirements.
Good security starts with visibility.
Because if you cannot see what is happening within your environment, neither can you effectively protect it.
To learn more about Continent 8’s managed detection and response capabilities, or to discuss your logging and monitoring strategy, contact your account manager.
By Craig Lusher, Principal Solutions Architect, Continent 8 Technologies. Part of our Cybersecurity Awareness Month series exploring today’s most important cybersecurity challenges and opportunities.
Most technology teams have a mental list of security improvements they would like to make: a penetration test, a phishing exercise, a vulnerability assessment, or simply an independent view of where they stand.
The challenge is rarely identifying what needs to be done. More often, it’s finding the budget and time to do it. Security initiatives can easily fall behind more immediate business priorities, especially when everything appears to be running smoothly.
The problem is that security gaps rarely announce themselves in advance. Small investments can uncover weaknesses long before they become incidents, but many organisations delay taking that first step because they assume it requires a significant new budget.
For Cybersecurity Awareness Month, there’s a simple question worth asking: are you making the most of the security resources you already have available?
That’s the thinking behind Loyalty+, Continent 8 Technologies’ customer rewards programme.
Every dollar a customer spends across Continent 8’s portfolio, whether for cloud, infrastructure, connectivity, managed services, security or intelligence, automatically earns credits. There is no separate sign-up process, and each credit is worth one dollar (or local currency equivalent) that can be redeemed against security services.
For contracts of 12 months or longer, credits for the full contract term are granted upfront once the service is delivered, giving customers immediate access to funds that can be used to strengthen their security posture from day one.
Those credits can be applied to a wide range of services, including vulnerability assessments, penetration testing, phishing simulation campaigns, cyber maturity assessments and security audits. They can also be used towards ongoing solutions such as managed detection and response, web application firewall services, dark web monitoring and managed security operations.
We designed Loyalty+ around a simple principle: customers should be able to direct value where it matters most to their business. Rather than treating security as an additional cost to justify later, the programme helps organisations invest in reducing risk using benefits they may already have available.
The broader lesson extends beyond Continent 8. Before deciding the next security step is out of reach, take a closer look at the programmes, services and resources that already exist within your supplier ecosystem. You may be closer to improving your security posture than you think.
And if you’re a Continent 8 customer, it’s worth checking whether you have Loyalty+ credits available. Unused credits expire after 12 months, turning a potential security improvement into a missed opportunity.
Not sure what your Loyalty+ balance is or how it can be used? Contact your Continent 8 account manager to learn more and explore the security services available through the programme.
New cloud data center combines modular edge architecture, global connectivity and regulatory compliance for operators and suppliers
Continent 8 Technologies, a leading provider of cutting‑edge managed IT solutions designed for the global iGaming and online sports betting industry, has officially opened its new data center facility at Tioga Downs Casino Resort in Nichols, New York.
Developed specifically to meet the technical, operational and regulatory requirements of New York’s online sports betting market, the purpose-built facility provides a secure and compliant environment for licensed operators and approved B2B suppliers serving one of the most significant regulated wagering jurisdictions in North America. Designed as a specialist edge data center, it reflects Continent 8’s approach of delivering industry-specific infrastructure close to the regulated markets it serves, rather than relying on large-scale hyperscale deployments.
Built using Continent 8’s modular design approach, the facility launches with approximately 500kW of capacity and 24 racks, with the ability to expand to 48 racks as customer demand grows. The site is supported by resilient power, cooling, connectivity and security systems and is fully managed by Continent 8.
The New York site extends the company’s unbeatable North American footprint and provides customers with direct access to the company’s private global network, which spans more than 100 locations across five continents, including 30+ US states.
New York is the largest regulated online sports betting market in the United States, generating more than $26 billion in wagers during 2025 alone. The facility has been developed to support the operators and suppliers serving this market, including leading brands such as FanDuel, delivering the infrastructure, connectivity and services required both for today’s operations and tomorrow’s technology requirements.
As operators increasingly explore AI-enabled applications across areas such as customer experience, operations and security, the edge deployment forms part of Continent 8’s broader strategy to support innovation within regulated environments.
Michael Tobin, Founder and Chairman at Continent 8 Technologies, said: “The future of infrastructure for our industry isn’t about building ever-larger facilities. It’s about delivering the right infrastructure in the right locations to support highly regulated markets.”
“New York is a perfect example of that approach. This facility has been developed specifically for the needs of regulated online sports betting operators and suppliers, providing the foundation they need to participate and innovate within the market.”
“We believe edge infrastructure will play an increasingly important role in the future of online sports betting, and we’re proud to be continuing that journey with this opening.”
Mike Small, Chief Executive Officer at Continent 8 Technologies, said: “Operators and suppliers increasingly need more than hosting infrastructure. They need a partner that can support connectivity, cloud, cybersecurity and emerging technologies through a single integrated platform.”
“This facility combines local market presence with access to Continent 8’s global network and managed services capabilities, helping customers deploy, scale and innovate with confidence.”
“As demand continues to grow, we’re looking forward to supporting both existing customers and new entrants as they expand their presence in the market.”
The new deployment reinforces Continent 8’s strategy of delivering market-specific infrastructure that helps operators and suppliers scale with confidence.